
October 4, 2026
Google OSS VRP stops accepting product bug reports amid AI-generated submissions
As of Oct 1, 2026, Google has stopped accepting new product vulnerability reports in its OSS VRP program.
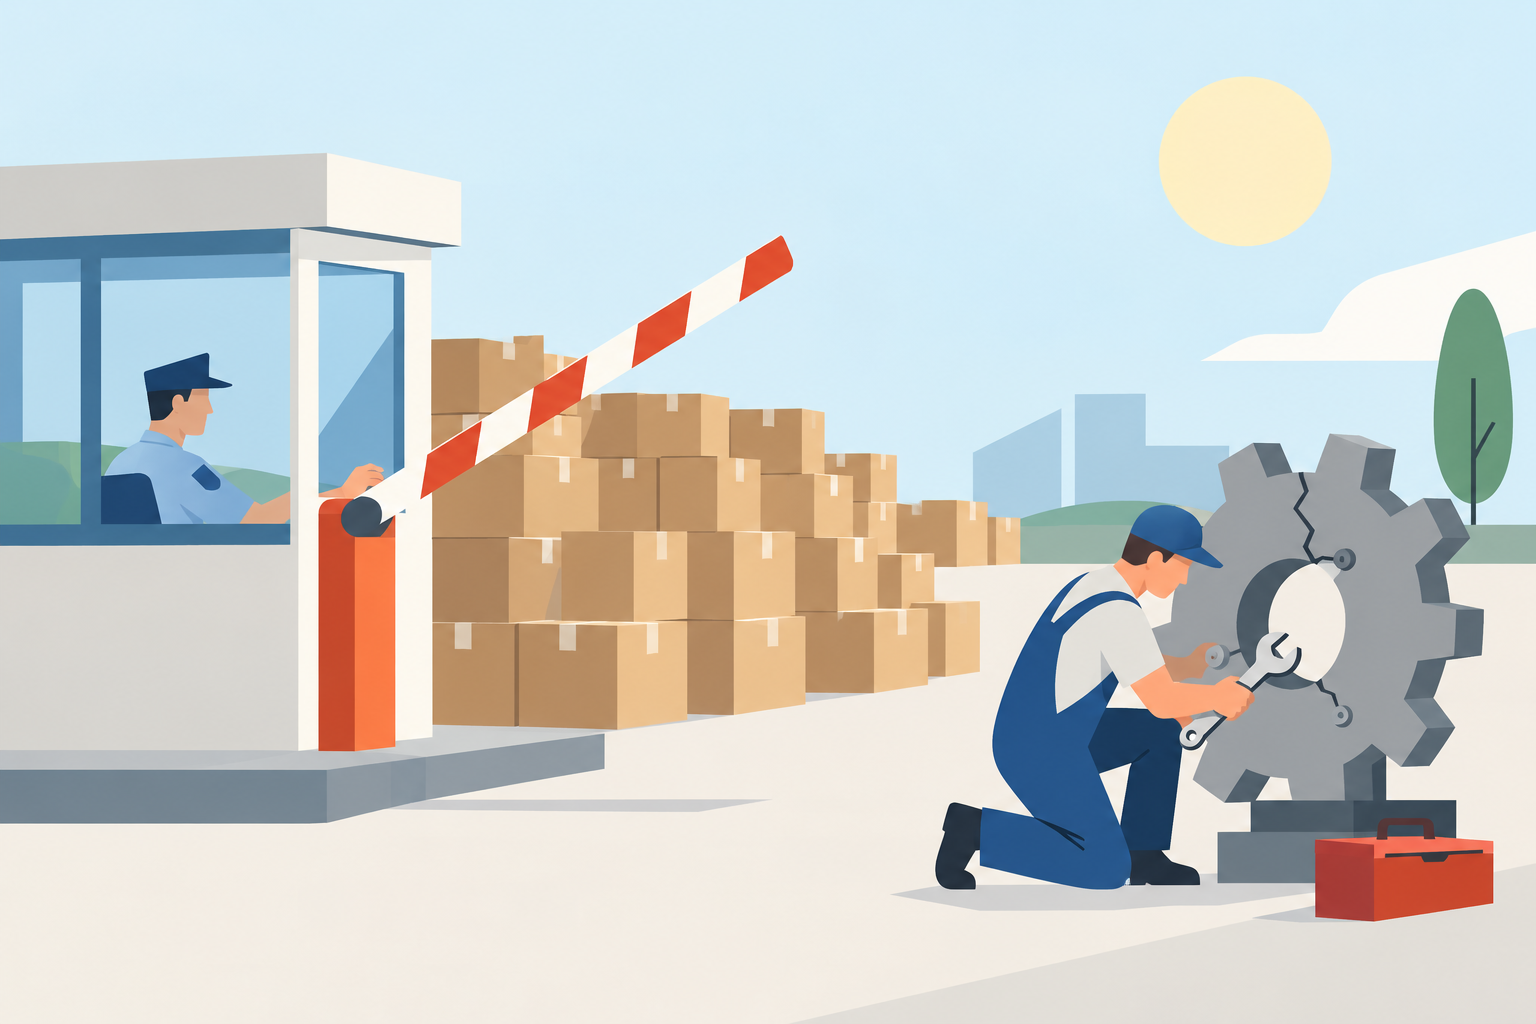
Google attributed the pause to a sharp rise in automated submissions, the vast majority of them invalid. OSS VRP rewards vulnerabilities found in Google's open source projects. The company continues to accept and review previously filed reports as well as reports of software supply chain attacks.
The rules had already been tightened. Back on Mar 19, Google reported a surge of AI-generated reports with made-up bugs and findings with no meaningful security impact. For memory corruption bugs in the OT0 and OT1 project tiers, the company began requiring a reproduction through an existing OSS-Fuzz test or an already accepted fix.
In April, Google removed payouts and credit for product vulnerabilities and other security issues in the OT2 and OT3 tiers. It cut the maximum reward for a supply chain compromise in OT2 to $3,133.70. Now Google has paused intake of new product vulnerability reports altogether.
Other programs are still running. For some Google Cloud repositories, Cloud VRP remains available if the vulnerability affects Google Cloud products. In the vulnerability form, select Cloud VRP at the Bug Location step and attach a PoC, reproduction steps and an impact description.
Patch Rewards accepts open source security fixes. A submission usually requires an already merged GitHub pull request with a demonstrated security improvement to the project. A fix can be submitted with the Submit patch button on the program page.
Under the Patch Rewards rules as of Oct 1, base payouts for tier 1 depend on the complexity and value of the fix:
- $500. - $2,000. - $7,500. - $15,000.
Primary sources: [TechCrunch, Oct 4, 2026](https://techcrunch.com/2026/10/04/google-froze-its-open-source-bug-bounty-program-due-to-a-significant-rise-in-ai-submissions), [Tom’s Hardware, Oct 3, 2026](https://www.tomshardware.com/tech-industry/artificial-intelligence/google-suspends-part-of-the-oss-vrp-bug-bounty-program-due-to-an-influx-of-invalid-ai-submissions-product-vulnerability-submissions-ended-october-1), [Google's March and April rule changes](https://bughunters.google.com/blog/ossvrp-rule-updates-2026).
Google promises an update on the future of OSS VRP in Q1 2027.